Pentest Notes / Enumeration / Web Enumeration
Active
• ping
• traceroute or tracert
• telnet (not imp)
• nc (to grab banners during initial connection)
• Add domain to /etc/hosts: echo "[IP] [domain]" | sudo tee -a /etc/hosts
Linux : /etc/hosts
Windows : C:\Windows\System32\drivers\etc\hosts
Directories and file enumeration
gobuster dir -x html,txt,php,js -u http://[MACHINE_IP] -w /usr/share/wordlists/seclists/Discovery/Web-Content/medium.txt
gobuster dir -x php,txt,html,js -u http://[MACHINE_IP] -w /usr/share/wordlists/dirb/medium.txt
ffuf -ic -e .html,.txt,.php,.js -u http://[MACHINE_IP] -w /usr/share/wordlists/seclists/Discovery/Web-Content/medium.txt
Subdomain Enumeration
gobuster dns --domain [example.thm] -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-5000.txt
ffuf -ic -H "Host: FUZZ.acmeitsupport.thm" -u http://[MACHINE_IP] -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-5000.txt
use ip address, sometimes the name wont work even after adding it to /etc/hosts
Filter by size of response:
ffuf -ic -H "Host: FUZZ.[domain]" -u http://[MACHINE_IP] -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-5000.txt -fs [size]
dnsenum --enum [domain] -f /usr/share/seclists/Discovery/DNS/subdomains-top1million-20000.txt -r
-r : enables recursive brute forcing
Virtual Host Enumeration
gobuster vhost -u http://[MACHINE_IP] --domain example.thm --append-domain -w /usr/share/wordlists/seclists/Discovery/DNS/subdomains-top1million-5000.txt
Fingerprinting
• Banner Grabbing
curl -I [domain]
• Analysing HTTP Headers
Look at: Server and X-Powered-By
• WhatWeb - Identify web technologies
whatweb [domain]
• Wafw00f - Identify WAFs
pip3 install git+https://github.com/EnableSecurity/wafw00f
wafw00f [domain]
• Nikto - Web scanner and used in fingerprinting tech stack of website
sudo apt update && sudo apt install -y perl
git clone https://github.com/sullo/nikto
cd nikto/program
chmod +x ./nikto.pl
nikto -h [domain] -Tuning b
-Tuning b tells Nikto to only run the Software Identification modules.
Crawling
Popular crawlers - Burp suite spider, OWASP ZAP, Scrapy (Python frameworl) and Apache Nutch (Scalable)
Custom crawler using Scapy:
python3 -m venv venv
source ./venv/bin/activate
pip3 install scrapy
wget -O ReconSpider.zip https://cdn.services-k8s.prod.aws.htb.systems/content/modules/144/ReconSpider.v1.2.zip
unzip ReconSpider.zip && rm ReconSpider.zip
python3 ReconSpider.py http://[domain]
Output : results.json contains emails, links, external_files, js_files, form_fields, images, video, audio and comments
Automated Recon
• FinalRecon: All-in-one modular web recon
• Recon-ng: Modular recon framework
• theHarvester: Email and subdomain harvester
• SpiderFoot: Automated OSINT collection
• OSINT Framework: Curated OSINT resource directory
FinalRecon
git clone https://github.com/thewhiteh4t/FinalRecon.git
cd FinalRecon; python3 -m venv venv; source ./venv/bin/activate
pip3 install -r requirements.txt
chmod +x ./finalrecon.py
./finalrecon.py --help
DNS Zone Transfers
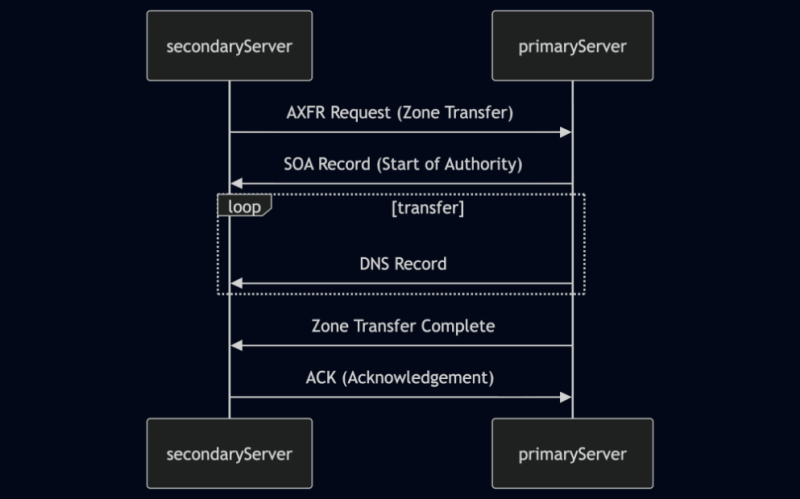
Exploiting Zone Transfers
dig axfr @nsztm1.digi.ninja zonetransfer.me
Instructs dig to request a full zone transfer (axfr) from the DNS server responsible for zonetransfer.me.
FeroxBuster
Discovers unlinked content in web applications
Install: curl -sL https://raw.githubusercontent.com/epi052/feroxbuster/main/install-nix.sh | sudo bash -s $HOME/.local/bin
API Fuzzing
git clone https://github.com/PandaSt0rm/webfuzz_api.git
cd webfuzz_api
pip3 install -r requirements.txt
python3 api_fuzzer.py http://[MACHINE_IP]:[PORT]
https://tryhackme.com/room/modernwebstacks
Fingerprinting MERN
Header check:
| Signal | Value | Confidence | Comment |
|---|---|---|---|
| X-Powered-By header | Express | High | Express sends by default, absent only if app.disable('x-powered-by') is called |
| Set-Cookie header | connect.sid=s%3A... | High | Absence of this doesn't mean absence of express |
| Unhandled route response | Cannot GET /nonexistent (plain text) | High | curl -I [MACHINE_IP]:3000/nonexistent : Returns plaintext rather than error |
Fingerprinting Next.js
Possible CVE: CVE-2025-29927 and CVE-2025-55182
| Signal | Value | Confidence |
|---|---|---|
| X-Powered-By header | Next.js | High |
| HTML source | window.__next_f in script tag | High (confirms App Router) |
| Static asset paths | /_next/static/chunks/ | High |
| Middleware headers | x-middleware-next or x-middleware-rewrite | Medium |
| Redirect to protected route | HTTP 307 to /login | Medium |
Add the header "x-middleware-subrequest: middleware:middleware:middleware:middleware:middleware" to bypass middleware check
Fingerprinting Django
Possible CVE: CVE-2021-35042
| Signal | Value | Confidence |
|---|---|---|
| Server header | WSGIServer/0.2 CPython/X.X.X | High |
| Cookie name | csrftoken | High |
| X-Frame-Options header | DENY | High |
| X-Content-Type-Options header | nosniff | High |
| Referrer-Policy header | same-origin | Medium |
| HTML source (any POST form) | csrfmiddlewaretoken hidden field | High |
The combination of X-Frame-Options: DENY, X-Content-Type-Options: nosniff, and Referrer-Policy: same-origin appearing together signals Django's SecurityMiddleware.
Fingerprinting LAMP
| Signal | Value | Confidence |
|---|---|---|
| Server header | Apache/2.4.49 (Unix) | High - exact CVE match |
| 404 error page footer | Apache/2.4.49 version string | High |
| /cgi-bin/ response | 403 Forbidden (not 404) | High - mod_cgi enabled |